
Loading
Loading
We use strictly necessary cookies to run this site, and analytics cookies to understand how it's used. See our Privacy Policy for details.
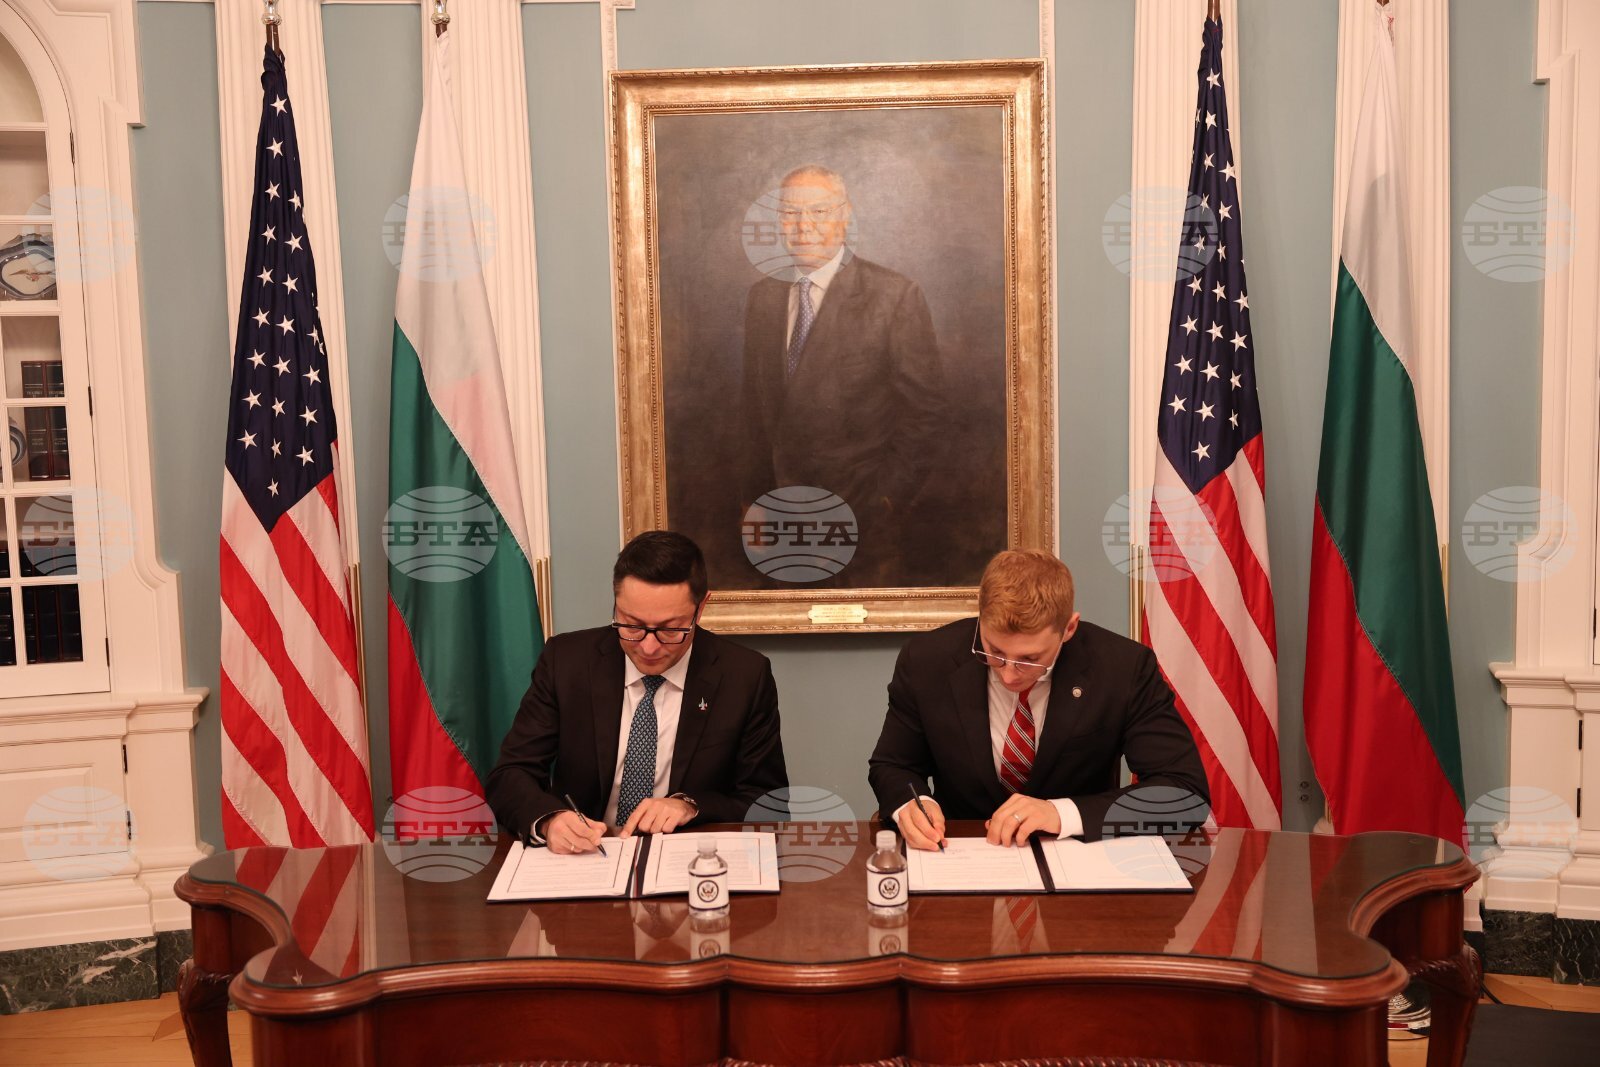
Bulgaria and the United States have signed a joint declaration on cooperation in artificial intelligence (AI), the Bulgarian Economy Ministry said Wednesday.
Summary
Deputy Prime Minister and Economy, Investments and Industry Minister Alexander Poulev and US Under Secretary of State for Economic Affairs Jacob Helberg signed the document in Washington. The US-initiated declaration, endorsed by 54 countries, aims to promote AI innovation, secure digital infrastructure, reliable supply chains and investment in AI infrastructure. During his visit, Poulev met with US State Department representatives, including Assistant Secretary of State for Political-Military Affairs Fleet White, to discuss bilateral strategic cooperation, Black Sea security, defence and space technology.
At his meeting with US Under Secretary of State for Economic Affairs Jacob Helberg, he discussed expanding bilateral economic ties, attracting US investment in strategic sectors, and developing artificial intelligence and high technology. Poulev highlighted Bulgaria’s IT ecosystem, engineering talent and research capacity, including the Institute for Computer Science, Artificial Intelligence and Technology (INSAIT), as assets for attracting investment and expanding cooperation with US companies. Priority areas include electric vehicles and batteries, data centres, AI infrastructure, space technology and cybersecurity.
The talks also covered the F-16 Block 70 fighter aircraft programme and joint industrial cooperation projects. Poulev said Bulgaria was committed to strengthening its strategic partnership with the US and expanding high-value-added manufacturing. Poulev is leading a delegation of 30 representatives from 20 companies on a US business mission organized by the American Chamber of Commerce in Bulgaria, focused on cooperation in strategic and high-tech sectors.
KazaSec's take
AI-related security incidents are a genuinely new category, prompt injection, model manipulation, and data leakage through an LLM integration don't map cleanly onto traditional application security testing, and are worth assessing deliberately rather than assuming existing controls already cover them.
Coverage details
We've archived 52 other articles touching the same topic (world) , see the full security news archive.
Relevant from KazaSec
More coverage on this topic
We help organizations find and fix the gaps before they make headlines.