
Loading
Loading
We use strictly necessary cookies to run this site, and analytics cookies to understand how it's used. See our Privacy Policy for details.
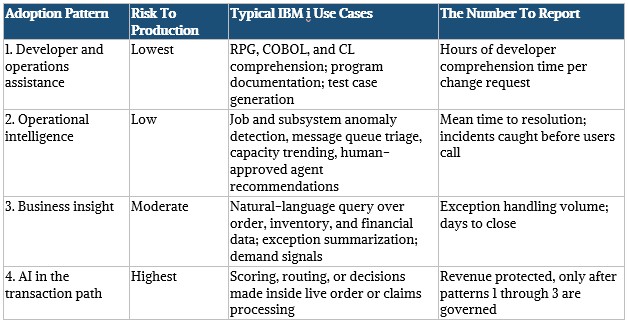
The AI conversation has arrived at the IBM i shop, and in most cases, it did not come in through the computer room door.
Summary
It came down from the boardroom, or over from finance, or sideways from a sales vice president who watched a demo at a conference and wants to know why the company cannot ask its own order history a question in plain English. The IBM i manager is then handed a question that sounds technical but is strategic: can our core platform play in this, or do we need to replace it to get there?
This is a brief wire summary, the full story (linked below) has the complete details.
KazaSec's take
AI-related security incidents are a genuinely new category, prompt injection, model manipulation, and data leakage through an LLM integration don't map cleanly onto traditional application security testing, and are worth assessing deliberately rather than assuming existing controls already cover them.
Coverage details
We've archived 265 other articles touching the same topic (watsonx.data, sql, it jungle) , see the full security news archive.
Related security advisories
Relevant from KazaSec
More coverage on this topic
We help organizations find and fix the gaps before they make headlines.