
Loading
Loading
We use strictly necessary cookies to run this site, and analytics cookies to understand how it's used. See our Privacy Policy for details.
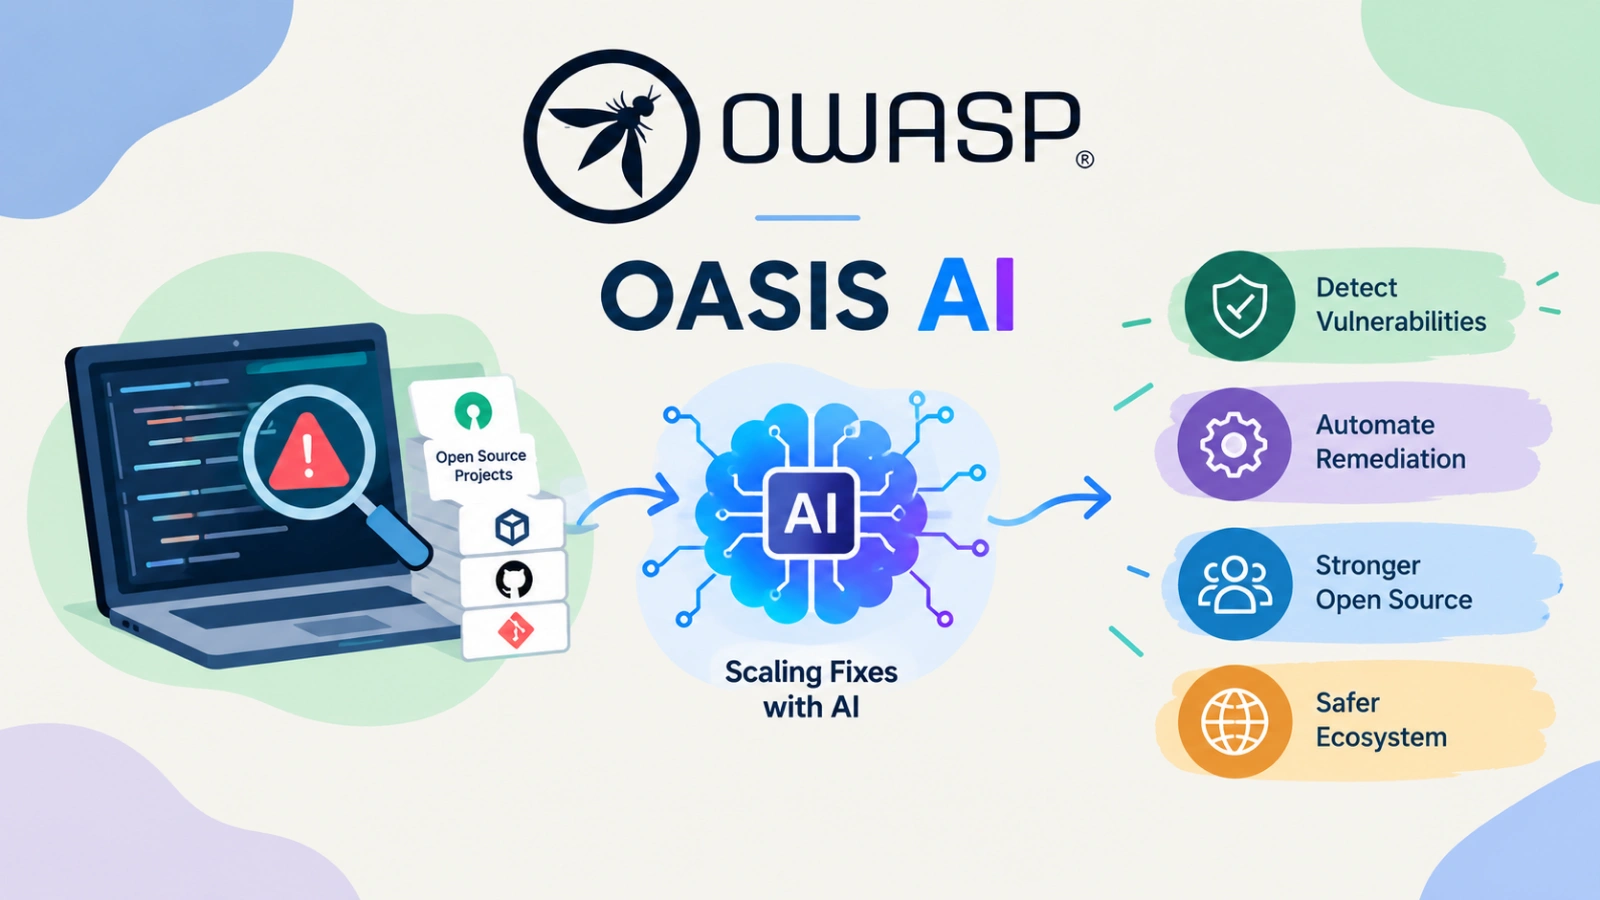
OWASP has launched the Open Automated Security Initiative for Software (OASIS), a global community effort designed to close the gap between finding vulnerabilities in open source code and actually fixing them.
Summary
Announced on August 26, 2026, in San Francisco, the initiative pairs AI-generated fix candidates with human validation from application security professionals, aiming to deliver
This summary is a partial excerpt, the source's own feed cuts off here. Read the full story at Cybersecuritynews for the rest.
KazaSec's take
A newly disclosed vulnerability is only a real risk to your organization once it's confirmed present and exploitable in your own environment, not every CVE applies equally to every network. Knowing the difference is exactly what a proper vulnerability assessment is for.
Coverage details
We've archived 192 other articles touching the same topic (cyber security news) , see the full security news archive.
Relevant from KazaSec
More coverage on this topic
We help organizations find and fix the gaps before they make headlines.