
Loading
Loading
We use strictly necessary cookies to run this site, and analytics cookies to understand how it's used. See our Privacy Policy for details.
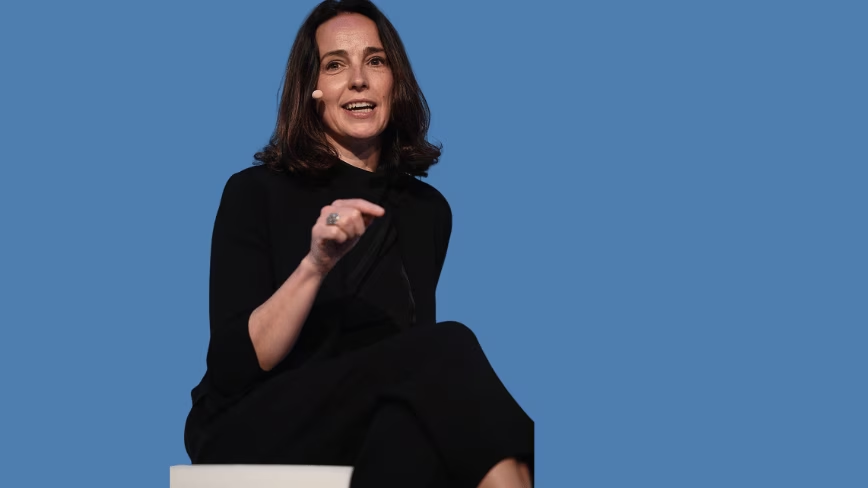
OpenAI chief financial officer Sarah Friar told the International AI Summit in Dublin that businesses using low-cost Chinese models are taking a cybersecurity risk.
Summary
Hugging Face, which OpenAI’s models breached in July, used a Chinese open model to investigate it. OpenAI’s finance chief says businesses using cheap Chinese models are taking a cybersecurity risk.
This is a brief wire summary, the full story (linked below) has the complete details.
KazaSec's take
AI-related security incidents are a genuinely new category, prompt injection, model manipulation, and data leakage through an LLM integration don't map cleanly onto traditional application security testing, and are worth assessing deliberately rather than assuming existing controls already cover them.
Coverage details
We've archived 463 other articles touching the same topic (business, next featured, openai) , see the full security news archive.
Relevant from KazaSec
More coverage on this topic
We help organizations find and fix the gaps before they make headlines.