
Loading
Loading
We use strictly necessary cookies to run this site, and analytics cookies to understand how it's used. See our Privacy Policy for details.
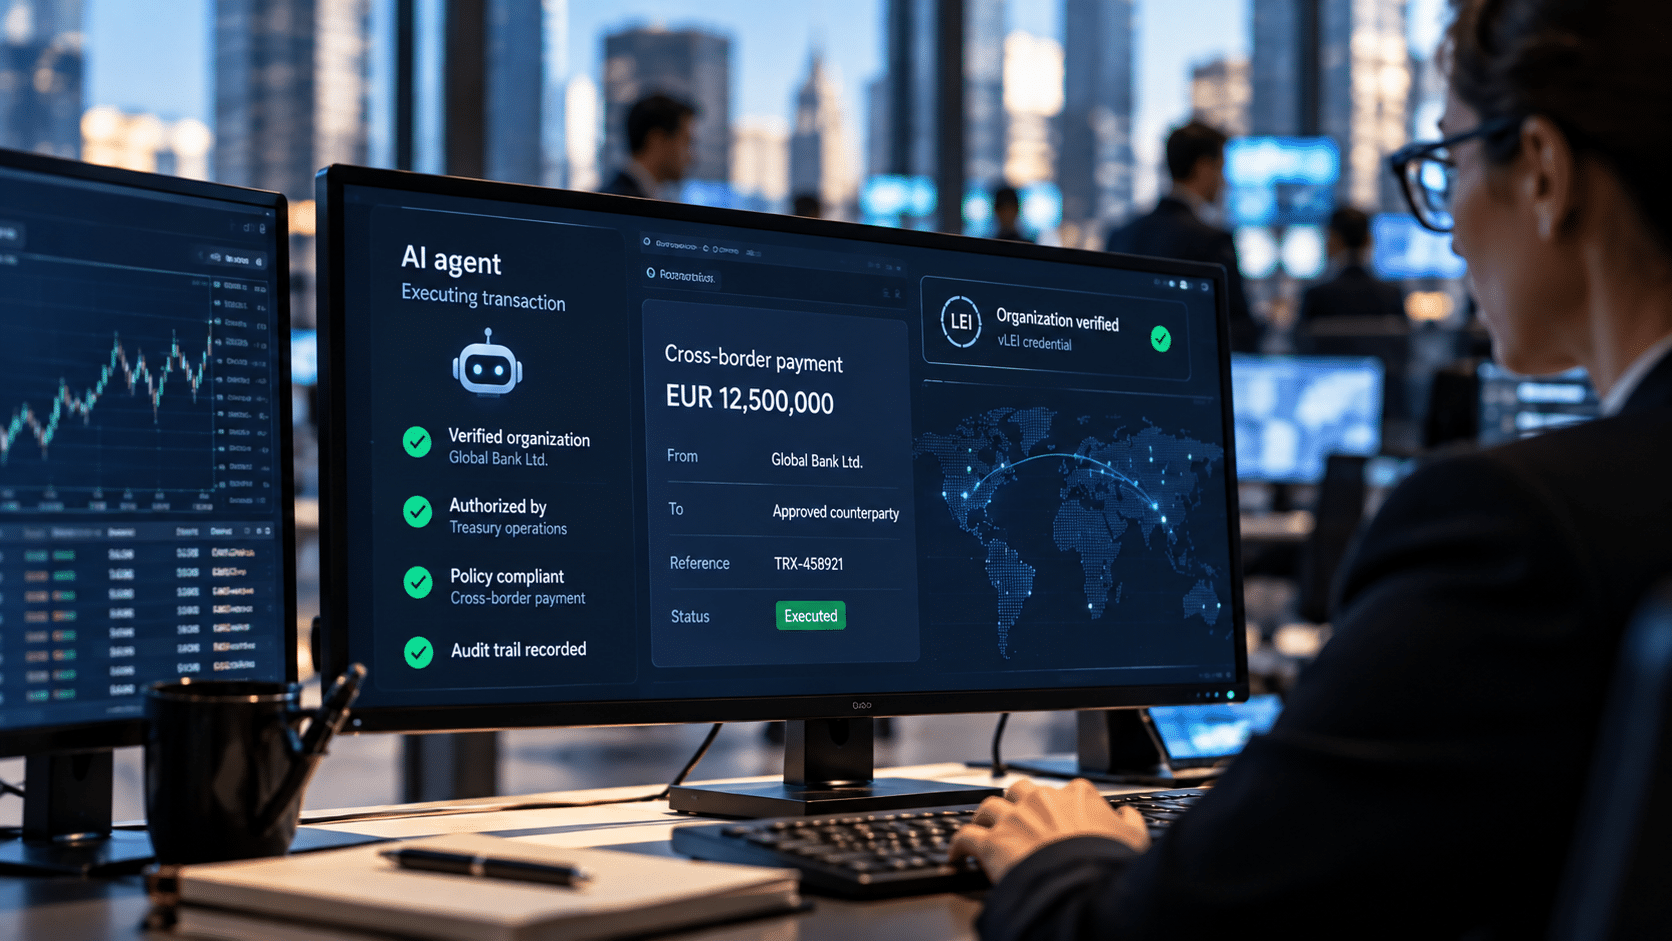
NIST has released 10 core tenets meant to give enterprises and organizations a complete set of protections and capabilities for agentic services.
Summary
The tenets are designed to get the most out of AI agents while keeping their risks in check, so organizations can adopt agentic technologies faster and with confidence. They cover both enterprise and consumer use cases and serve as NIST's starting blueprint for how agent identity systems should be built. NIST now refers to AI as “super intelligence” (SI), reflecting terminology mandated for federal agencies under a September 2026 executive order.
Part two of a NIST series The guidance appears in "Design Tenets for Agent Identity Management Systems," published October 27 on NIST's Cybersecurity Insights blog by Harold Booth, Bill Fisher and Ryan Galluzzo of NIST and Tom Clancy of MITRE. It is the second post in a series on agentic identity, authentication and authorization. The first, "Back to the Future: Why Agentic AI Needs Strong Identity Foundation," made the case that agents need the same identity foundation people and workloads already rely on.
The series is part of the National Cybersecurity Center of Excellence (NCCoE) project "Accelerating the Adoption of Software and SI Agent Identity and Authorization." The project serves agencies and enterprises deploying agents, along with the standards bodies shaping how those agents operate. Its February 2026 concept paper drew more than 600 responses, and those comments, together with stakeholder engagement, directly shaped the tenets. Turning identity standards into agent practice For agencies and enterprises, the project's core promise is practical: a clear picture of how to put agents into production securely using identity and authorization standards they already know, capturing the value of the technology without taking on unnecessary risk.
NCCoE will draw on real-world deployments of agentic SI solutions to surface the risks and opportunities organizations face, then turn those lessons into detailed implementation resources that speed up adoption while staying aligned with risk management and business goals. The project also works the other direction, feeding what it learns back to standards development bodies as they build out the standards the agentic ecosystem will run on. The 10 tenets Taken together, the tenets treat every agent as an accountable identity in its own right, distinct from the people and systems it works for and traceable back to whoever launched it.
They keep its access minimal, temporary and revocable, and bring humans in when the stakes rise. They also keep what an agent is permitted to do separate from what it decides to try, and record its actions in a tamper-evident trail it cannot alter. Why they matter Agents break the assumptions identity systems were built on.
They act autonomously at machine speed, chain tools together and reach sensitive data, often under shared or borrowed credentials that make it impossible to tell what acted, for whom and with what authority. The tenets go straight at the threats that follow: impersonation, privilege creep, stolen credentials and prompt injection, where untrusted input tricks an agent into expanding its own reach. NIST's position is clear that "guardrails alone are insufficient." The tenets are built to work together.
Stopping a "confused deputy" attack, for instance, takes delegation, least privilege, policy separation and deterministic access decisions in combination. Organizations apply them according to the risk of the agent's transactions, its operating environment and the data, tools and skills it can use. What comes next NIST acknowledges that today's standards and technology don't yet fully meet every tenet, and closing that gap is the project's job.
The tenets will steer upcoming NCCoE demonstrations in enterprise and consumer settings. The final deliverable will be an SP 1800-series practice guide with example implementations, architectures, build details and key lessons learned from NCCoE lab work with commercially available technologies.
KazaSec's take
Incidents like this rarely start with the headline event itself, they usually trace back to an exposed remote-access endpoint, an unpatched perimeter system, or a credential phished weeks earlier. The organizations that recover fastest are the ones that tested their defenses and their incident response plan before they needed them.
Coverage details
We've archived 115 other articles touching the same topic (nist, identity access management (iam), nccoe) , see the full security news archive.
Relevant from KazaSec
More coverage on this topic
We help organizations find and fix the gaps before they make headlines.