
Loading
Loading
We use strictly necessary cookies to run this site, and analytics cookies to understand how it's used. See our Privacy Policy for details.
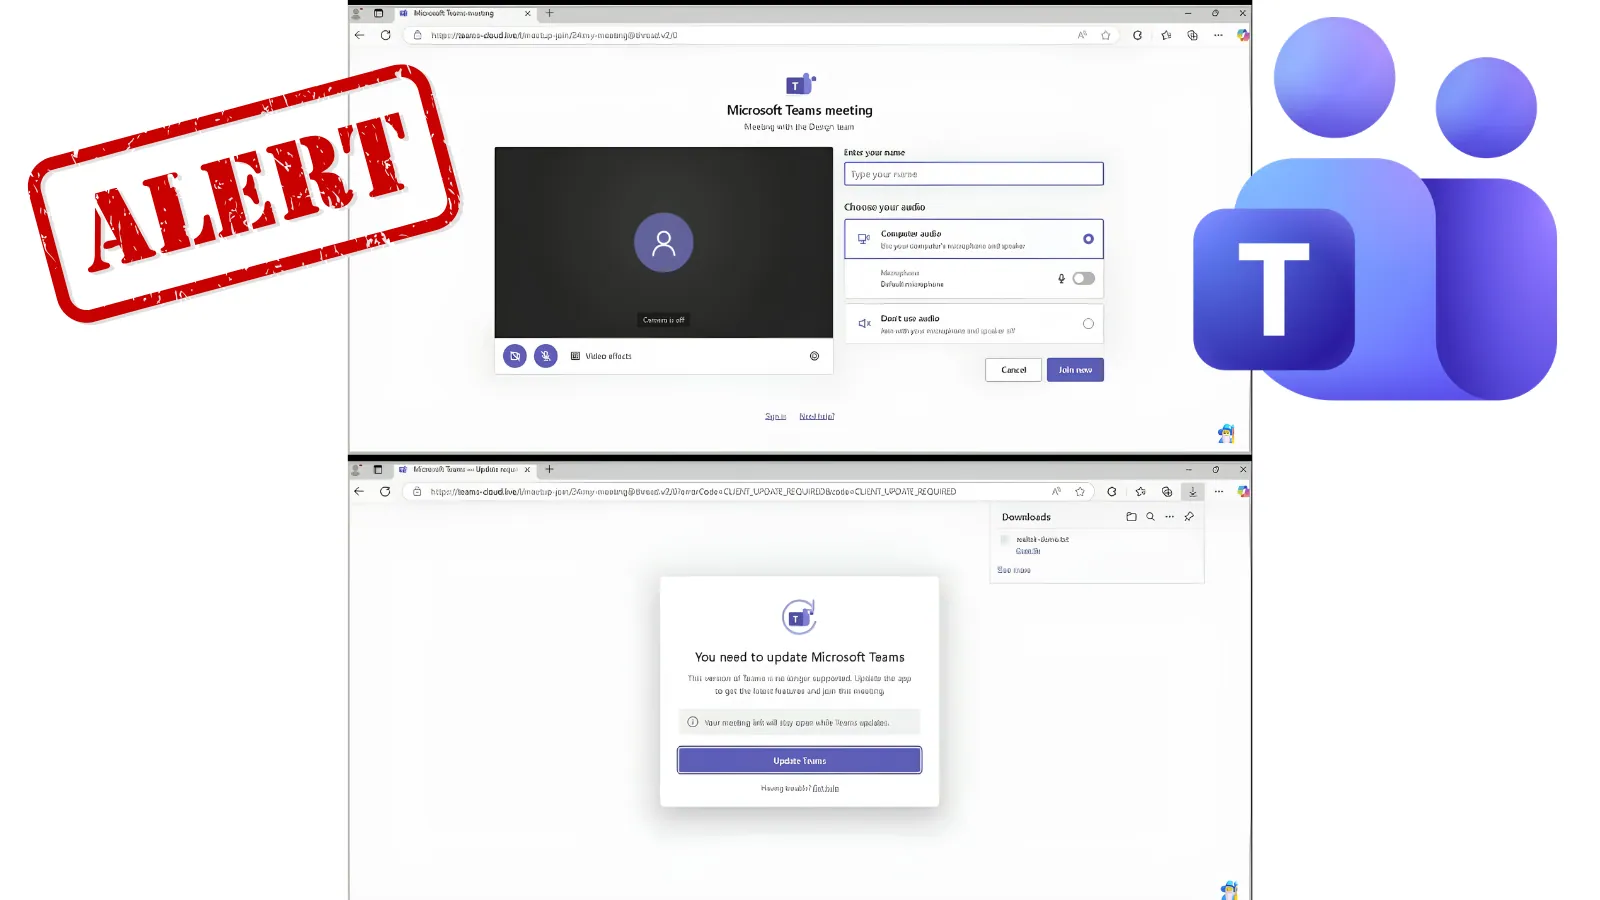
A newly registered domain copies Microsoft Teams’ login page and interface, raising concerns about a phishing attempt targeting workplace users.
Summary
Security researcher Steven Lim reported that teams-cloud[.]live was just five days old when he flagged it on October 18, 2026. He urged organizations to block the address before employees encounter the fake site.
This is a brief wire summary, the full story (linked below) has the complete details.
KazaSec's take
Phishing and credential-based attacks succeed because they target people, not just infrastructure, technical controls like SPF, DKIM, and DMARC only ever close part of that gap. The rest comes down to whether a team can actually spot the fake, and whether a compromised credential can still be reused anywhere else.
Coverage details
We've archived 224 other articles touching the same topic (cyber security, microsoft, cyber security news) , see the full security news archive.
Related security advisories
Relevant from KazaSec
More coverage on this topic
We help organizations find and fix the gaps before they make headlines.