
Loading
Loading
We use strictly necessary cookies to run this site, and analytics cookies to understand how it's used. See our Privacy Policy for details.
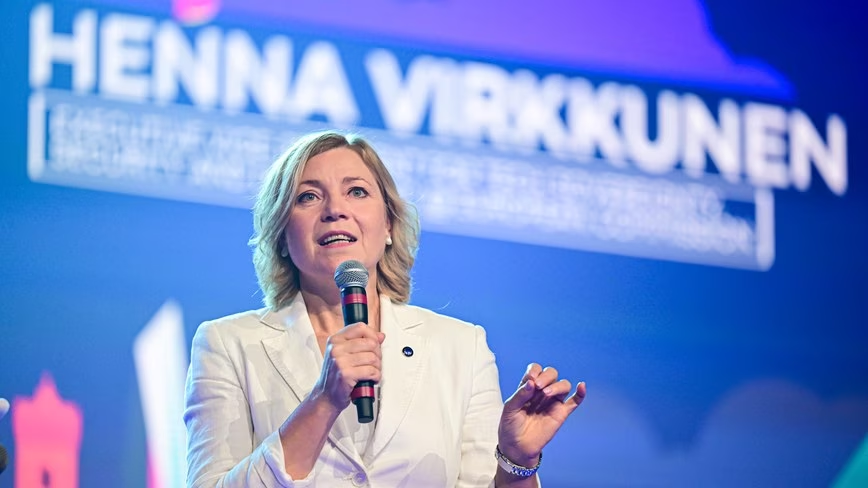
“Our AI Office has started enforcing these rules, and sent Requests for Information addressing issues such as security, external evaluation and monitoring how models are used,” EU tech chief Henna Virkkunen said in a speech in Dublin on 14 October.
Summary
The AI Office has sent such requests to OpenAI and Anthropic, Euronews reports.
This is a brief wire summary, the full story (linked below) has the complete details.
KazaSec's take
AI-related security incidents are a genuinely new category, prompt injection, model manipulation, and data leakage through an LLM integration don't map cleanly onto traditional application security testing, and are worth assessing deliberately rather than assuming existing controls already cover them.
Coverage details
We've archived 466 other articles touching the same topic (legal, data and security, government and policy) , see the full security news archive.
Relevant from KazaSec
More coverage on this topic
We help organizations find and fix the gaps before they make headlines.