
Loading
Loading
We use strictly necessary cookies to run this site, and analytics cookies to understand how it's used. See our Privacy Policy for details.
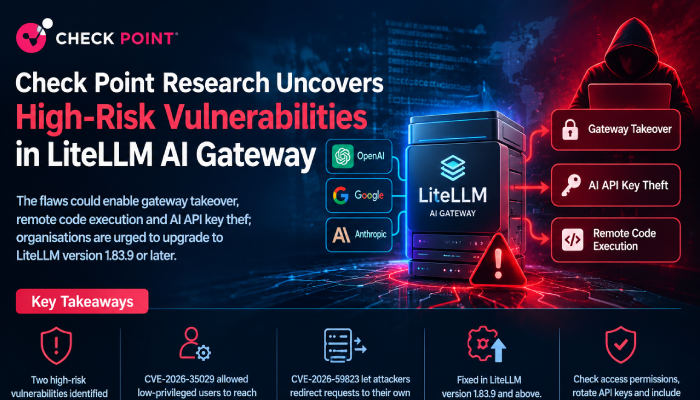
The flaws could enable gateway takeover, remote code execution and AI API key theft; organisations are urged to upgrade to LiteLLM version 1.83.9 or later.
Summary
Check Point Research has identified two high-risk vulnerabilities in LiteLLM, an open-source large language model (LLM) gateway used to connect applications with AI providers such...
This is a brief wire summary, the full story (linked below) has the complete details.
KazaSec's take
A newly disclosed vulnerability is only a real risk to your organization once it's confirmed present and exploitable in your own environment, not every CVE applies equally to every network. Knowing the difference is exactly what a proper vulnerability assessment is for.
Coverage details
Related security advisories
Relevant from KazaSec
More security news
We help organizations find and fix the gaps before they make headlines.