
Loading
Loading
We use strictly necessary cookies to run this site, and analytics cookies to understand how it's used. See our Privacy Policy for details.
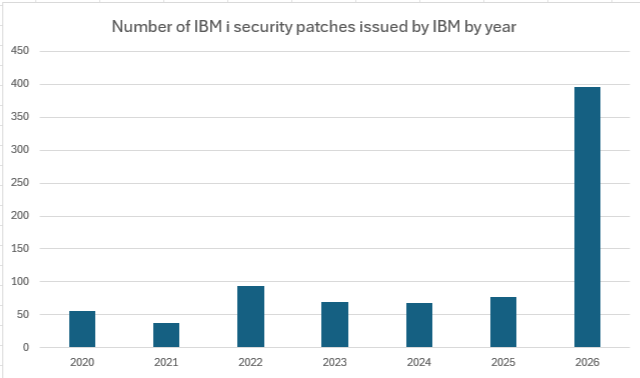
IBM has issued nearly 400 security alerts for IBM i so far in 2026, a 5X increase compared to all of 2025.
Summary
IBM says the big uptick in alerts and associated security patches is due to a general increase in security vulnerabilities across the industry, and is not due to its use of AI to help it find flaws and get patches into the hands of customers. If you follow the IBM i PTF Guide on a weekly basis – which is highly recommended – you may have noticed more security alerts and patches this year.
This is a brief wire summary, the full story (linked below) has the complete details.
KazaSec's take
A newly disclosed vulnerability is only a real risk to your organization once it's confirmed present and exploitable in your own environment, not every CVE applies equally to every network. Knowing the difference is exactly what a proper vulnerability assessment is for.
Coverage details
We've archived 9 other articles touching the same topic (ptf, ibm i, rational developer for i) , see the full security news archive.
Related security advisories
Relevant from KazaSec
More coverage on this topic
We help organizations find and fix the gaps before they make headlines.