
Loading
Loading
We use strictly necessary cookies to run this site, and analytics cookies to understand how it's used. See our Privacy Policy for details.
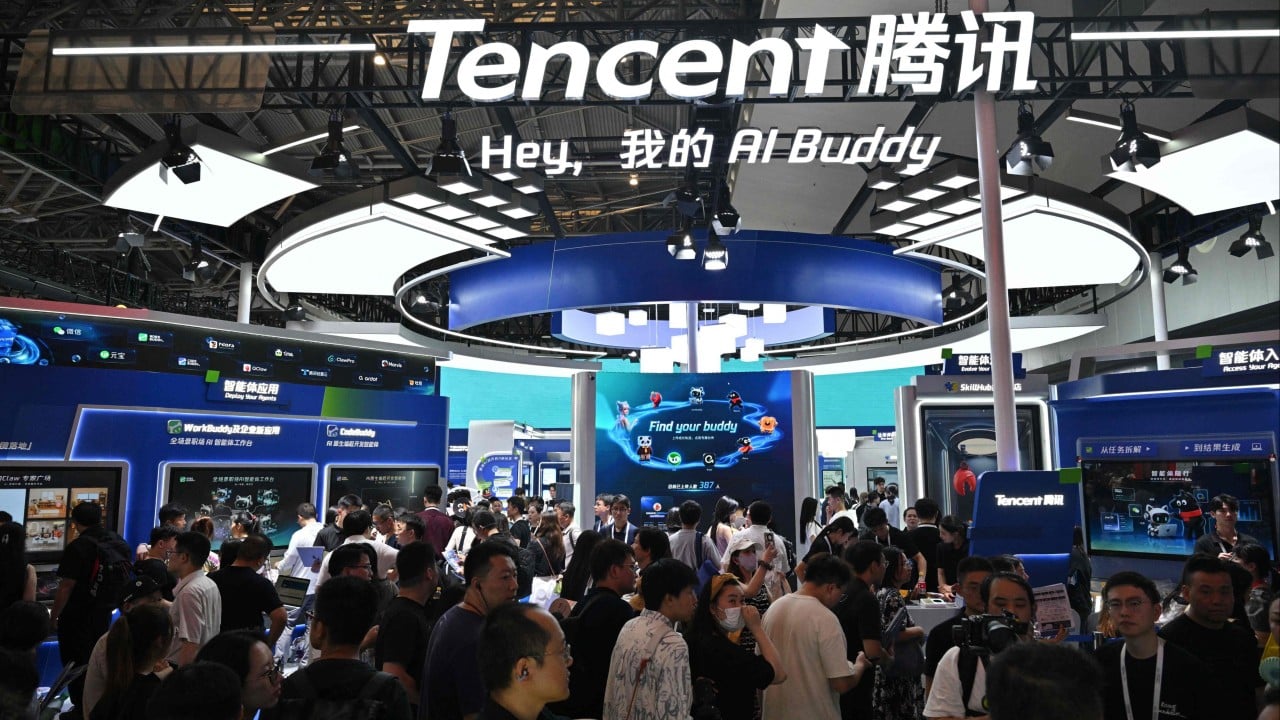
A fleet of artificial intelligence agents operating on a Tencent Holdings cloud platform made thousands of attempts to circumvent security protections on Alibaba Group Holding’s mapping service, according to findings by third-party researchers.
Summary
It is one of the first reported “rogue” AI events involving Chinese companies, following a string of recent high-profile incidents in the US, including from OpenAI and Anthropic, highlighting the risks of increasingly autonomous AI systems. Agents running...
This is a brief wire summary, the full story (linked below) has the complete details.
KazaSec's take
Most public cloud incidents trace back to a misconfiguration, an overly permissive IAM role, a storage bucket left open, a default setting nobody revisited, rather than a flaw in the cloud provider itself. A cloud security review is built to catch exactly that class of mistake before it's found the hard way.
Coverage details
We've archived 511 other articles touching the same topic (united states, tencent holdings, hong kong) , see the full security news archive.
Relevant from KazaSec
More coverage on this topic
We help organizations find and fix the gaps before they make headlines.